


Overissued refers to a condition where a cryptocurrency, token, or digital asset has been created or minted in quantities exceeding the originally defined or intended supply cap. Overissuance can occur due to smart contract bugs, protocol exploits, governance failures, or unauthorized use of minting privileges.
A transparently approved change to issuance rules is a separate governance decision, not necessarily an exploit.
In the blockchain context, overissuance is a critical concern because most crypto assets derive value partly from their scarcity properties – a token that was supposed to have a fixed supply of 21 million units but is found to have 22 million due to an exploit fundamentally undermines the trust and economic model of the entire project.
Overissuance events have historically caused severe market crashes and protocol crises, making strong supply controls a cornerstone of sound tokenomics design.
Origin & History
| Date | Event |
|---|---|
| 2010 | Bitcoin value overflow incident: a bug created 184 billion BTC before being patched via soft fork |
| 2016 | The DAO exploit transfers existing ETH; it is a contrast with overissuance, not an example of new ETH being minted |
| 2018 | Multiple ERC-20 tokens found vulnerable to batchOverflow bug, enabling unlimited token minting |
| 2019 | Stellar burns existing XLM; reducing supply is not an overissuance incident |
| 2020 | Cover Protocol exploit allows attacker to mint unlimited COVER tokens, crashing price 97% |
| 2021 | PAID Network suffers unauthorized minting of roughly 59.5 million PAID tokens |
| 2022 | Acala stablecoin aUSD overissued by approximately 3.02 billion tokens due to a misconfiguration exploit |
| 2023 | Multiple DeFi protocols implement supply monitoring and circuit breakers to prevent overissuance |
How It Works
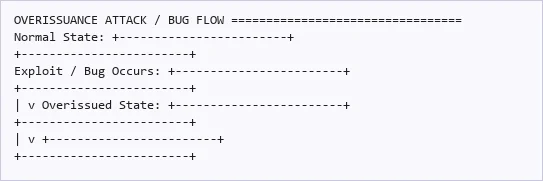
| Token Supply: 1,000,000 |
|---|
| Max Cap: 1,000,000 |
| Status: VALID |
| Attacker finds mint |
|---|
| function vulnerability |
| OR |
| Integer overflow bug |
| OR |
| Governance key |
| compromise |
| Token Supply: 5,000,000 | <– 4M extra tokens minted |
|---|---|
| Max Cap: 1,000,000 | |
| Status: OVERISSUED |
| Consequences: |
|---|
| – Price crash |
| – Trust destroyed |
| – Fork/rollback needed |
| Cause | Mechanism | Example |
|---|---|---|
| Smart Contract Bug | Integer overflow or unchecked mint function | BEC Token batchOverflow (2018) |
| Protocol Exploit | Reentrancy or logic flaw in minting logic | Cover Protocol infinite mint (2020) |
| Governance Attack | Compromised admin key triggers unauthorized minting | Paid Network exploit (2021) |
| Authorized Supply Changes | A valid governance change may alter issuance rules | Distinguish disclosed policy changes from unauthorized minting |
| Bridge Exploit | Wrapped tokens minted without backing on source chain | Wormhole bridge hack (2022) |
In Simple Terms
- Unexpected supply: Unauthorized minting can dilute holders and undermine confidence. The price effect depends on the scale of the incident, circulating supply, and remediation.
- Supply rules: Some assets have a cap; others use ongoing issuance. Overissuance means exceeding the applicable rules, not simply having an uncapped supply.
- Bug or Attack: Overissuance typically happens through software bugs (accidental) or exploits (malicious) rather than intentional design changes.
- Market impact: An overissuance incident can trigger a sharp price fall, but the magnitude and timing are not automatic.
- Hard to Fix: Recovering from overissuance often requires hard forks, token migrations, or community-wide consensus on remediation – all costly and contentious processes.
Real-World Examples
| Scenario | Implementation | Outcome |
|---|---|---|
| Bitcoin Value Overflow (2010) | Bug allowed creation of 184 billion BTC in a single transaction | Emergency soft fork deployed within hours; invalid block rejected by network |
| Cover Protocol (2020) | Attacker exploited staking contract to mint unlimited COVER tokens | Price crashed 97%; protocol launched replacement token via migration |
| Paid Network (2021) | Unauthorized minting creates roughly 59.5 million PAID tokens | Attacker dumped tokens for $3M; project redeployed with new token contract |
| Acala aUSD (2022) | A configuration error creates billions of unbacked aUSD; the project’s reports trace approximately 3.02 billion error-minted tokens (Source: Acala incident report) | Stablecoin de-pegged; Acala froze affected wallets and burned excess tokens |
Advantages
| Advantage | Description |
|---|---|
| Awareness Catalyst | Overissuance incidents drive industry-wide improvements in smart contract security |
| Audit Motivation | Fear of overissuance motivates thorough code audits and formal verification |
| Supply Monitoring | Prompts development of real-time supply monitoring and alert systems |
| Governance Reform | Incidents lead to better access controls and multi-sig requirements for minting functions |
Disadvantages & Risks
| Disadvantage | Description |
|---|---|
| Value Destruction | Unexpected issuance can dilute holders and reduce market confidence |
| Trust Collapse | Even after remediation, investor confidence may never fully recover |
| Legal Liability | Project teams may face lawsuits from holders whose investments were diluted |
| Chain Split Risk | Fixing overissuance may require controversial hard forks |
| Cascading Failures | Overissued tokens used as collateral in DeFi can trigger liquidation cascades |
Risk Management Tips:
- Invest in tokens with audited smart contracts and capped mint functions
- Monitor on-chain supply metrics and set alerts for unusual minting activity
- Diversify holdings to limit exposure to any single token’s overissuance risk
- Prefer tokens with immutable supply caps enforced at the protocol level
- Check if the project has admin keys that could trigger unauthorized minting
FAQ
Q: How is overissuance different from normal inflation?
A: Normal inflation is planned and transparent (like Ethereum’s issuance schedule). Overissuance is unintended supply creation beyond the defined parameters, typically from bugs or exploits.
Q: Can Bitcoin be overissued?
A: Bitcoin nodes enforce issuance rules, but software bugs can threaten those rules. The 2010 value-overflow incident created invalid excess supply that was removed through a corrective update. Bitcoin Core also fixed a critical inflation vulnerability in 2018; the disclosure did not identify exploitation on mainnet. (Source: Bitcoin inflation-vulnerability disclosure)
Q: What should I do if a token I hold gets overissued?
A: Monitor official project channels for remediation plans. If a token migration is announced, follow instructions carefully. Consider the risk-reward of holding through the remediation versus exiting.
Q: How can smart contracts prevent overissuance?
A: Monitor official project channels for remediation plans. If a token migration is announced, follow instructions carefully. Consider the risk-reward of holding through the remediation versus exiting.
Q: Does overissuance always crash the token price?
A: No fixed price outcome is guaranteed. Market reaction depends on the amount created, whether it was sold, the credibility of remediation, and broader market conditions.
Conclusion
Overissued tokens require investigation into authorization, supply rules, and the cause of the issuance. Distinguishing a planned supply change from an exploit is essential to understanding the risk.
Further reading on UPay: Tokenomics explained; Wrapped tokens explained; How stablecoins work








